Skip to content
    English | العربية

    DPO as a Service / Saudi Arabia

    DPO as a Service in Saudi Arabia

    White Label Consultancy (WLC) acts as the appointed Data Protection Officer for organisations subject to the Personal Data Protection Law (PDPL) in Saudi Arabia. Our Saudi Arabia DPO service is led by Simon Leadbetter, Associate Partner for the GCC, and supported by a multi-jurisdiction privacy team in Europe and the Gulf.

    § 01Key facts

    Key facts: DPO requirements in Saudi Arabia

    Law
    Personal Data Protection Law (PDPL) and its Implementing Regulations
    Regulator
    Saudi Data and AI Authority (SDAIA)
    When a DPO is mandatory
    Public entities processing personal data at large scale, organisations whose core activities involve regular and systematic monitoring of individuals, and organisations whose core activities involve sensitive personal data (SDAIA DPO Rules, Article 5)
    Can the DPO be external
    Yes. The DPO may be an executive, an employee or an external contractor, appointed under a written agreement (Articles 4 and 6)
    Residency requirement
    The SDAIA DPO Rules set no residency requirement
    Registration or filing duty
    The appointment must be documented, and the DPO's contact details provided to SDAIA through the National Data Governance Platform and made available to data subjects.
    WLC lead DPO
    Simon Leadbetter, Associate Partner, GCC
    Location
    Saudi Arabia and the wider GCC
    Where DPO records are hosted
    Agreed with you at the start of the engagement, in line with your own policies and the PDPL transfer rules
    § 02The legal test

    Do we need a DPO under the Saudi PDPL?

    The PDPL became enforceable on 14 September 2024. In August 2024 SDAIA issued the Rules for Appointing a Personal Data Protection Officer, which set out when an organisation must appoint a DPO and what that person must bring.

    A DPO is mandatory in three situations: (1) the organisation is a public entity providing services that involve processing personal data on a large scale; (2) its core activities involve regular and systematic monitoring of individuals, for example tracking, location data, cookies, CCTV or behavioural analytics; or (3) its core activities involve processing sensitive personal data, such as health or credit data. Large scale is judged by the number of individuals, the volume and type of data, the geographical reach and the categories of individuals. Supporting activities, such as HR processing of employee data, do not count as core activities.

    Where a DPO is appointed, the rules set minimum requirements: appropriate academic qualifications, data protection experience, and knowledge of risk management and regulatory requirements. The appointment must be documented, and the DPO's contact details must be provided to SDAIA, through the National Data Governance Platform, and made available to data subjects.

    Official source: Saudi Data and AI Authority (SDAIA).

    § 03The service

    What WLC does as your DPO

    • Appointment and registration with the regulator
    • Records of processing activities
    • Data protection impact assessments (DPIAs)
    • Handling data subject requests
    • Personal data breach response
    • Transfer assessments for data leaving the jurisdiction
    • Staff training
    • Liaison with the regulator
    • Reporting to the board

    Your first 90 days

    1. Formal appointment, registration of the DPO's contact details and a kick-off with your key stakeholders.
    2. Review of current processing, records of processing and existing policies.
    3. Gap assessment against the law and a prioritised remediation plan.
    4. First board report and an agreed routine for DPIAs, requests and breaches.
    § 04Your named DPO

    Who your DPO is

    01
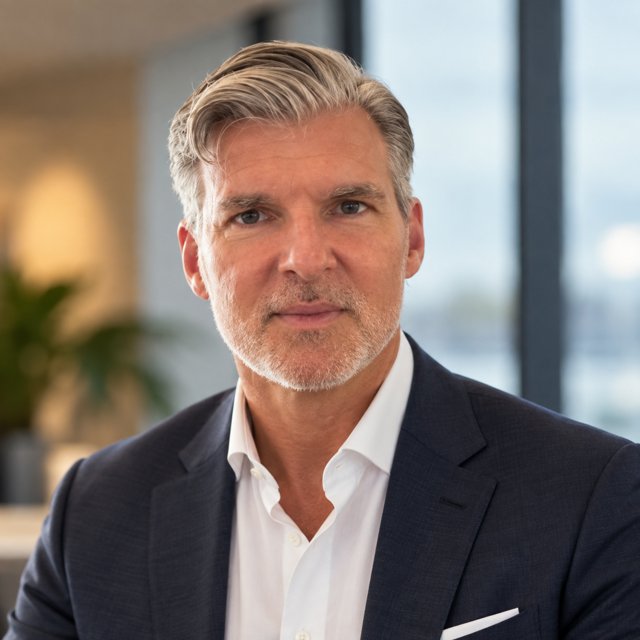
    Simon Leadbetter, Associate Partner, GCC, White Label Consultancy

    GCC

    Simon Leadbetter

    Associate Partner, GCC

    Simon is a lawyer and digital trust, governance and transformation programme director with 20 years of GRC experience across the UK and the GCC, spanning data protection, AI governance and regulatory frameworks. Before joining WLC, he served six years as Director of Personal Data Protection at NEOM, where he led enterprise privacy governance and PDPL compliance and helped define NEOM's AI Ethics Council, after leading the development of a draft data protection law, regulation and operating model for a new Saudi regulator. He previously spent 20 years at Accenture across the UK and the UAE, including building its data privacy centre of excellence for GDPR.

    Credentials: FIP, CIPP/E, CIPM.

    Meet the full team or see Simon's LinkedIn profile.

    § 05How we work

    Engagement models

    a

    WLC as your appointed DPO

    WLC is formally appointed as your Data Protection Officer. A named senior consultant holds the role, supported by the wider WLC team.
    b

    Support for an internal or group DPO

    You keep your own DPO. WLC provides advice, capacity and local regulatory knowledge when your DPO needs it.
    c

    Group DPO in Europe, local lead in the Gulf

    Your group DPO stays in Europe. WLC acts as the local data protection lead in the Gulf, so one programme covers both regions.
    § 06Why WLC

    Why organisations choose WLC

    • A named DPO with six years leading PDPL compliance at NEOM, a Saudi organisation.
    • Experience drafting a data protection law, regulation and operating model for a new Saudi regulator.
    • One team covering the Saudi PDPL, the UAE regimes and the GDPR, so group programmes stay consistent.

    Proof

    Client names are shared on request, subject to client approval.

    § 07Questions

    Frequently asked questions

    Do we need a DPO under the Saudi PDPL?

    It depends on your processing, and the triggers are set out in SDAIA's Rules for Appointing a Personal Data Protection Officer, issued in August 2024. A DPO is required where (1) the organisation is a public entity providing services that involve processing personal data on a large scale; (2) its core activities involve regular and systematic monitoring of individuals, for example tracking, location data, cookies, CCTV or behavioural analytics; or (3) its core activities involve processing sensitive personal data, such as health or credit data. Organisations outside these cases may appoint a DPO voluntarily, and must review periodically whether the requirement has started to apply. If any apply, the appointment must be documented and the DPO's contact details provided to SDAIA through the National Data Governance Platform.

    Can an external provider act as our DPO in Saudi Arabia?

    Yes. Article 4 of the SDAIA DPO Rules allows the DPO to be an executive, an employee or an external contractor, and Article 6 requires a written agreement with an external DPO. WLC can be appointed, with Simon Leadbetter as the named lead. The appointment is documented in the same way as an internal one, and the contact details registered with SDAIA are those of the appointed DPO.

    Does our DPO need to be based in Saudi Arabia?

    The SDAIA DPO Rules do not set a residency requirement. WLC's lead DPO for Saudi Arabia, Simon Leadbetter, works across Saudi Arabia and the wider GCC, and is supported by WLC colleagues in Europe and the Gulf. We will confirm with you how the residency position applies to your organisation before the appointment is made.

    How do we register our DPO with SDAIA?

    The DPO's contact details are provided to SDAIA through the National Data Governance Platform. The appointment itself must be documented, and the same contact details must be made available to data subjects, for example in your privacy notice. When WLC is appointed, we prepare the documentation and support you through the platform submission.

    What qualifications does a DPO need under the SDAIA rules?

    The SDAIA rules require appropriate academic qualifications, data protection experience, and knowledge of risk management and regulatory requirements. They set minimum requirements rather than one named certificate. WLC's lead DPO for Saudi Arabia is a lawyer holding the FIP, CIPP/E and CIPM certifications, with six years leading PDPL compliance at NEOM.

    Does appointing an external DPO transfer our legal responsibility?

    No. The controller remains responsible for complying with the PDPL, whoever holds the DPO role. An external DPO advises, monitors compliance, deals with SDAIA and data subjects, and reports to your management. Decisions on how personal data is processed, and accountability for them, stay with your organisation.

    Can our CISO or compliance officer also be the DPO?

    Article 9 of the SDAIA DPO Rules says the controller must not give the DPO tasks that conflict with the DPO role or affect the DPO's independence. In practice, the DPO should not hold a role that decides how personal data is processed, because that creates a conflict of interest. Where an internal person holds the role, WLC can support them so the independence of the function is maintained.

    How does the Saudi PDPL compare with the GDPR?

    The two laws share many concepts, including legal bases, data subject rights and transfer restrictions, but they differ in detail. Our comparative analysis of the GDPR and selected Middle East privacy laws sets out where they align and where they diverge, which helps groups that already run a GDPR programme extend it to Saudi Arabia.

    Can one DPO cover Saudi Arabia and our European entities?

    The SDAIA DPO Rules do not require the DPO to be based in Saudi Arabia, so a group DPO elsewhere is not ruled out, provided data subjects and SDAIA can reach them and they have the required knowledge of the PDPL. A common model is a group DPO in Europe with a local data protection lead in Saudi Arabia. WLC works in both regions, so it can provide the local lead, support your group DPO, or hold both roles where the law allows it.

    How quickly can WLC be appointed?

    Timing depends on how ready your documentation is, and we agree it with you at the outset. The engagement starts with the formal appointment, registration of the DPO's contact details and a kick-off with your stakeholders. The first 90 days then cover a review of current processing, a gap assessment and the first board report.

    Where are our DPO records stored?

    Records of processing, DPIAs, data subject requests and breach logs are the records a DPO keeps on your behalf. We agree with you at the start of the engagement where they are hosted and who can access them, so the arrangement suits your own policies.
    § 09Get in touch

    Talk to our Saudi Arabia DPO team

    Last reviewed: by Simon Leadbetter, Associate Partner, GCC