Skip to content
    English | العربية

    DPO as a Service / the DIFC

    DPO as a Service in the DIFC

    White Label Consultancy (WLC) acts as the appointed Data Protection Officer for organisations in the Dubai International Financial Centre (DIFC), under DIFC Data Protection Law No. 5 of 2020. The service is led by Simon Leadbetter, Associate Partner for the GCC, and delivered with WLC's Dubai office.

    § 01Key facts

    Key facts: DPO requirements in the DIFC

    Law
    DIFC Data Protection Law No. 5 of 2020 and the Data Protection Regulations
    Regulator
    DIFC Commissioner of Data Protection
    When a DPO is mandatory
    DIFC Bodies (other than the Courts), and controllers or processors that carry out High Risk Processing Activities on a systematic or regular basis (Article 16)
    Can the DPO be external
    Yes. The DPO may be an employee or provided under a service agreement, and one DPO may serve a group (Article 16)
    Residency requirement
    The DPO must reside in the UAE, unless they are employed in the group and perform a similar function for the group internationally (Article 16)
    Annual assessment
    Controllers with a DPO submit an annual assessment of their processing to the Commissioner (Article 18)
    Registration
    Controllers and processors notify the Commissioner and renew the notification each year
    AI and autonomous systems
    Regulation 10 sets rules for personal data processed through autonomous and semi-autonomous systems
    WLC lead DPO
    Simon Leadbetter, Associate Partner, GCC
    Local office
    Dubai
    § 02The legal test

    Do we need a DPO in the DIFC?

    DIFC Data Protection Law No. 5 of 2020 applies to entities registered in the DIFC, and to processing in the DIFC by others. It is enforced by the Commissioner of Data Protection.

    Under Article 16, a DPO is mandatory for DIFC Bodies, other than the Courts, and for controllers and processors that carry out High Risk Processing Activities on a systematic or regular basis. High Risk Processing includes, for example, processing that uses new technology with a high risk to individuals, large scale processing of special category data, and systematic and extensive profiling. Other organisations may appoint a DPO voluntarily.

    The DPO can be an employee or provided under a service agreement, and one DPO can serve several group entities. The DPO must reside in the UAE unless they are an employee of the group who performs a similar function for the group internationally. Where a DPO is appointed, the controller must also submit an annual assessment of its processing to the Commissioner.

    Official source: DIFC Data Protection.

    § 03The service

    What WLC does as your DPO

    • Appointment and registration with the regulator
    • Records of processing activities
    • Data protection impact assessments (DPIAs)
    • Handling data subject requests
    • Personal data breach response
    • Transfer assessments for data leaving the jurisdiction
    • Staff training
    • Liaison with the regulator
    • Reporting to the board
    • Annual assessment for the Commissioner
    • Regulation 10 assessments for AI and autonomous systems

    Your first 90 days

    1. Formal appointment, registration of the DPO's contact details and a kick-off with your key stakeholders.
    2. Review of current processing, records of processing and existing policies.
    3. Gap assessment against the law and a prioritised remediation plan.
    4. First board report and an agreed routine for DPIAs, requests and breaches.
    § 04Your named DPO

    Who your DPO is

    01
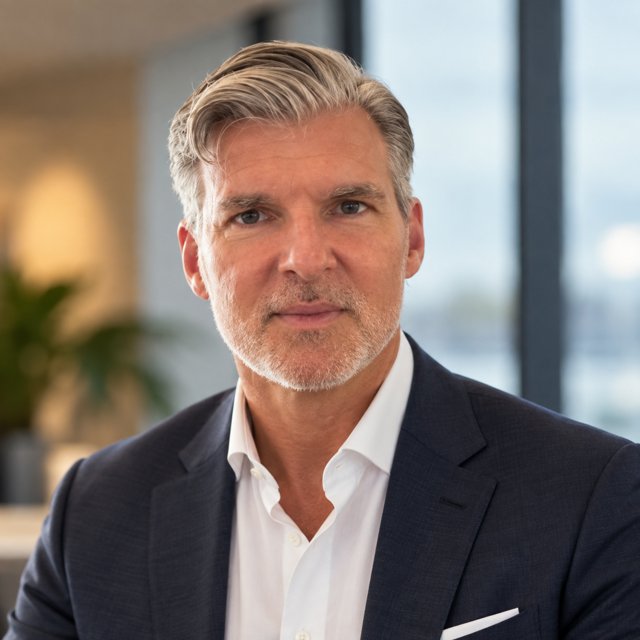
    Simon Leadbetter, Associate Partner, GCC, White Label Consultancy

    GCC

    Simon Leadbetter

    Associate Partner, GCC

    Simon is a lawyer and digital trust, governance and transformation programme director with 20 years of GRC experience across the UK and the GCC, spanning data protection, AI governance and regulatory frameworks. Before joining WLC, he served six years as Director of Personal Data Protection at NEOM, where he led enterprise privacy governance and PDPL compliance and helped define NEOM's AI Ethics Council, after leading the development of a draft data protection law, regulation and operating model for a new Saudi regulator. He previously spent 20 years at Accenture across the UK and the UAE, including building its data privacy centre of excellence for GDPR.

    Credentials: FIP, CIPP/E, CIPM.

    Meet the full team or see Simon's LinkedIn profile.

    § 05How we work

    Engagement models

    a

    WLC as your appointed DPO

    WLC is formally appointed as your Data Protection Officer. A named senior consultant holds the role, supported by the wider WLC team.
    b

    Support for an internal or group DPO

    You keep your own DPO. WLC provides advice, capacity and local regulatory knowledge when your DPO needs it.
    c

    Group DPO in Europe, local lead in the Gulf

    Your group DPO stays in Europe. WLC acts as the local data protection lead in the Gulf, so one programme covers both regions.
    § 06Why WLC

    Why organisations choose WLC

    • A Dubai office and experience with the DIFC regime, including Regulation 10 for AI systems.
    • A named DPO lead with six years leading data protection at NEOM and 20 years at Accenture across the UK and the UAE.
    • One team for the DIFC, the federal UAE law, ADGM and the GDPR, which suits financial groups with entities in several places.

    Proof

    Client names are shared on request, subject to client approval.

    § 07Questions

    Frequently asked questions

    Do we need a DPO in the DIFC?

    Article 16 of DIFC Data Protection Law No. 5 of 2020 requires a DPO for DIFC Bodies, other than the Courts, and for controllers and processors carrying out High Risk Processing Activities on a systematic or regular basis. Others may appoint one voluntarily.

    What counts as High Risk Processing in the DIFC?

    The law gives examples, including processing that uses new or different technology with a heightened risk to individuals, large scale processing of special category data, systematic and extensive evaluation of individuals such as profiling, and large scale monitoring of publicly accessible areas. Your specific processing should be assessed against the definition in the law.

    Can an external provider act as our DPO in the DIFC?

    Yes. Article 16 allows the DPO to be an employee or to be provided under a service agreement. A group can also appoint a single DPO for several entities.

    Does our DPO need to live in the UAE?

    Yes, in most cases. The DPO must reside in the UAE unless they are an individual employed within your group who performs a similar function for the group internationally. Before appointment we confirm with you who from WLC holds the role so this requirement is met.

    What is the DIFC annual assessment?

    Under Article 18, a controller that has appointed a DPO must submit an annual assessment of its processing activities to the Commissioner. As your DPO, WLC prepares the assessment and submits it with you.

    What is DIFC Regulation 10?

    Regulation 10 of the DIFC Data Protection Regulations covers personal data processed through autonomous and semi-autonomous systems, including AI. It adds notice, purpose and governance requirements. WLC also offers a dedicated Regulation 10 certification service.

    Do we need to register with the DIFC Commissioner?

    Yes. Controllers and processors in the DIFC must notify the Commissioner of their processing and renew the notification each year. WLC keeps the notification aligned with your records of processing.

    Does appointing an external DPO transfer our legal responsibility?

    No. The controller remains responsible for complying with the law. The DPO advises, monitors and works with the Commissioner, while decisions about processing stay with your organisation.

    § 09Get in touch

    Talk to our DIFC DPO team

    Last reviewed: by Simon Leadbetter, Associate Partner, GCC