Skip to content

    The GCC practice · Dubai 25.20°N

    Governance, risk and compliance across all six Gulf states.

    Partner-led advice from Dubai for Saudi Arabia, the UAE, Qatar, Bahrain, Oman and Kuwait.

    Regulation in the Gulf has moved from emerging to enforced, and it now reaches well beyond data. Boards answer to corporate governance codes, regulators expect a working compliance function, and supervisors look at third parties, resilience, data, security and AI together. We work for Gulf organisations and for the international groups that operate here.

    Saudi Arabia →UAE →

    Also covered: Qatar · Bahrain · Oman · Kuwait

    Arabian GulfSaudi ArabiaUAEQatarBahrainOmanKuwait
    • DIFC-approved Accredited Certification Body for Regulation 10
    • Office at Dubai World Trade Centre
    • Partner who led NEOM's PDPL compliance programme
    • All six GCC states covered

    discuss a GCC engagement →

    § 01The national agenda

    Compliance that serves the national goals.

    Saudi Vision 2030

    Trusted data and responsible AI are part of the Kingdom's plan. We align PDPL, NDMO data governance and the SDAIA AI Ethics Principles so that compliance supports digital growth rather than slowing it.

    UAE AI Strategy 2031 and We the UAE 2031

    The UAE wants to lead in AI adoption. We build AI governance that lets you move quickly and still answer to the UAE Data Office, the DIFC Commissioner and the ADGM Office of Data Protection.

    Where data and AI sit

    Data location and sovereign processing can decide a public-sector or regulated deal. We map where your data and models are hosted and document the transfer basis before it becomes a gate.

    § 02The rules we cover

    Country by country.

    The rules differ in detail and converge in intent. We design one governance and control framework and document where each regime genuinely diverges.

    01

    Saudi Arabia

    Our view: the most demanding regime in the region. Expect SAMA and NCA to test controls in practice, and treat PDPL as fully enforced.

    Governance and compliance: CMA Corporate Governance Regulations · SAMA rules and compliance function requirements · anti-money-laundering and counter-terrorist financing obligations · Competition Law

    Resilience and cyber: SAMA Cyber Security Framework and Business Continuity Management Framework · NCA Essential Cybersecurity Controls

    Data and AI: Personal Data Protection Law (PDPL) and implementing regulations · NDMO data governance · SDAIA AI Ethics Principles

    02

    UAE, federal

    Our view: most groups face several regimes at once. Map federal, free-zone and sector rules together and run one programme.

    Governance and compliance: SCA corporate governance rules for listed companies · CBUAE regulations and standards · anti-money-laundering law and sanctions obligations · Competition Law

    Resilience and cyber: UAE Information Assurance Standards · business continuity expectations of sector regulators

    Data and AI: Federal Decree-Law 45 of 2021 (PDPL) · Child Digital Safety Law · UAE Charter for AI

    03

    UAE, DIFC

    Our view: the most active supervisor in the region, and the first to regulate AI systems directly.

    Governance and compliance: DFSA rulebook, including governance, systems and controls, and compliance and MLRO functions

    Data and AI: DIFC Data Protection Law 2020 · Regulation 10 on autonomous and semi-autonomous systems

    04

    UAE, ADGM

    Our view: close to GDPR, so a European programme adapts well, but FSRA expects its own evidence.

    Governance and compliance: FSRA rulebook, including governance, compliance and anti-money-laundering requirements

    Data: ADGM Data Protection Regulations 2021

    05

    Qatar

    Our view: QFC and onshore rules differ. Decide early which applies to each entity.

    Governance and compliance: QFMA Governance Code · QCB regulations · anti-money-laundering law

    Cyber and data: National Information Assurance standard · Personal Data Privacy Protection Law · QFC Data Protection Regulations

    06

    Bahrain

    Our view: the CBB rulebook is the real driver for financial firms, with data protection built on top.

    Governance and compliance: Corporate Governance Code · CBB rulebook, including compliance, business continuity and cyber requirements

    Data: Personal Data Protection Law

    07

    Oman

    Our view: the executive regulations now apply in full. Processing permits and DPO duties need attention.

    Governance and compliance: CMA Code of Corporate Governance · Central Bank of Oman requirements

    Data: Personal Data Protection Law and executive regulations

    08

    Kuwait

    Our view: rules are sector-led. Banks and telecoms carry the heaviest obligations today.

    Governance and compliance: CMA Corporate Governance rules · Central Bank of Kuwait instructions · anti-money-laundering law

    Cyber and data: National Cyber Security Center requirements · CBK cybersecurity framework · CITRA Data Privacy Protection Regulation

    § 03Our view on enforcement

    What is live now, and what it means.

    Our reading of where each regime stands today. It is a summary, not legal advice, and the rules move quickly.

    Saudi Arabia

    The PDPL has been enforceable since September 2024. SDAIA expects registration, records and breach reporting to be in place, and has consulted on amendments to the implementing regulations. Treat it as a mature regime.

    UAE, federal

    The PDPL is in force, but its executive regulations are still awaited. Build the programme now, because sector regulators already expect controls and the regulations can arrive with a short runway.

    DIFC and ADGM

    The most active data protection supervisors in the region, with a track record of fines and published decisions. DIFC Regulation 10 brings AI systems into scope.

    Qatar, Bahrain, Oman, Kuwait

    Frameworks are in place and enforcement is building. Oman's executive regulations now apply in full, and Kuwait's data privacy regulation from CITRA covers telecoms and digital service providers.

    Download our GCC mid-year review →

    § 05Who leads it
    01
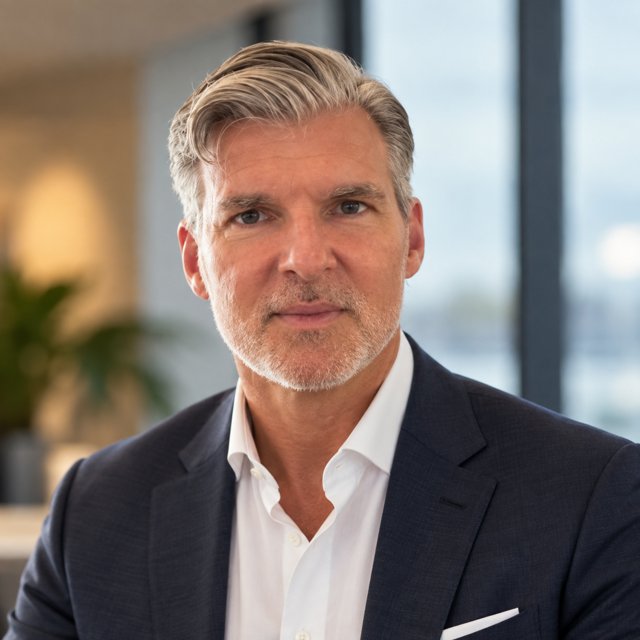
    Simon Leadbetter, Associate Partner, GCC, White Label Consultancy

    Associate Partner

    Simon Leadbetter

    Associate Partner, GCC

    Simon is a lawyer and digital trust, governance and transformation programme director with 20 years of GRC experience across the UK and the GCC, spanning data protection, AI governance and regulatory frameworks. Before joining WLC, he served six years as Director of Personal Data Protection at NEOM, where he led enterprise privacy governance and PDPL compliance and helped define NEOM's AI Ethics Council, after leading the development of a draft data protection law, regulation and operating model for a new Saudi regulator. He previously spent 20 years at Accenture across the UK and the UAE, including building its data privacy centre of excellence for GDPR. Simon holds the FIP, CIPP/E and CIPM certifications.

    Dubai office: +971 558 701 959, Dubai World Trade Center, Sheikh Zayed Road. Meet the full team.