Skip to content
    English | العربية

    DPO as a Service / ADGM

    DPO as a Service in ADGM

    White Label Consultancy (WLC) acts as the appointed Data Protection Officer for organisations in Abu Dhabi Global Market (ADGM), under the ADGM Data Protection Regulations 2021. The service is led by Simon Leadbetter, Associate Partner for the GCC, with WLC's Dubai office and our privacy team in Europe.

    § 01Key facts

    Key facts: DPO requirements in ADGM

    Law
    ADGM Data Protection Regulations 2021
    Regulator
    ADGM Office of Data Protection, led by the Commissioner of Data Protection
    When a DPO is mandatory
    Public authorities, organisations whose core activities need regular and systematic monitoring of individuals on a large scale, and organisations whose core activities involve large scale processing of special category data
    Can the DPO be external
    Yes. The DPO may be a staff member or work under a service contract, and a group may appoint one DPO
    Contact details
    The DPO's contact details must be published and communicated to the Commissioner
    Model
    Closely modelled on the EU GDPR, so group GDPR programmes carry over well
    WLC lead DPO
    Simon Leadbetter, Associate Partner, GCC
    Local office
    Dubai
    § 02The legal test

    Do we need a DPO in ADGM?

    The ADGM Data Protection Regulations 2021 apply to entities established in ADGM and to processing carried out in ADGM. They are enforced by the ADGM Office of Data Protection.

    A DPO is mandatory where the controller or processor is a public authority, where its core activities consist of processing that needs regular and systematic monitoring of individuals on a large scale, or where its core activities consist of large scale processing of special category data. These triggers follow the GDPR.

    The DPO can be a staff member or work under a service contract, and a group can appoint one DPO if each entity can reach them easily. The DPO's contact details must be published and communicated to the Commissioner.

    Official source: ADGM Office of Data Protection.

    § 03The service

    What WLC does as your DPO

    • Appointment and registration with the regulator
    • Records of processing activities
    • Data protection impact assessments (DPIAs)
    • Handling data subject requests
    • Personal data breach response
    • Transfer assessments for data leaving the jurisdiction
    • Staff training
    • Liaison with the regulator
    • Reporting to the board

    Your first 90 days

    1. Formal appointment, registration of the DPO's contact details and a kick-off with your key stakeholders.
    2. Review of current processing, records of processing and existing policies.
    3. Gap assessment against the law and a prioritised remediation plan.
    4. First board report and an agreed routine for DPIAs, requests and breaches.
    § 04Your named DPO

    Who your DPO is

    01
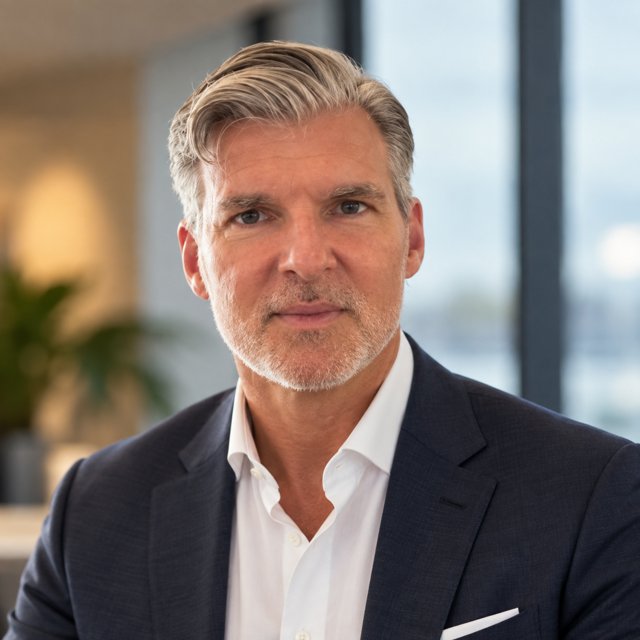
    Simon Leadbetter, Associate Partner, GCC, White Label Consultancy

    GCC

    Simon Leadbetter

    Associate Partner, GCC

    Simon is a lawyer and digital trust, governance and transformation programme director with 20 years of GRC experience across the UK and the GCC, spanning data protection, AI governance and regulatory frameworks. Before joining WLC, he served six years as Director of Personal Data Protection at NEOM, where he led enterprise privacy governance and PDPL compliance and helped define NEOM's AI Ethics Council, after leading the development of a draft data protection law, regulation and operating model for a new Saudi regulator. He previously spent 20 years at Accenture across the UK and the UAE, including building its data privacy centre of excellence for GDPR.

    Credentials: FIP, CIPP/E, CIPM.

    Meet the full team or see Simon's LinkedIn profile.

    § 05How we work

    Engagement models

    a

    WLC as your appointed DPO

    WLC is formally appointed as your Data Protection Officer. A named senior consultant holds the role, supported by the wider WLC team.
    b

    Support for an internal or group DPO

    You keep your own DPO. WLC provides advice, capacity and local regulatory knowledge when your DPO needs it.
    c

    Group DPO in Europe, local lead in the Gulf

    Your group DPO stays in Europe. WLC acts as the local data protection lead in the Gulf, so one programme covers both regions.
    § 06Why WLC

    Why organisations choose WLC

    • Deep GDPR experience in Europe, which maps directly onto a GDPR based regime like ADGM's.
    • A named DPO lead with six years leading data protection at NEOM and 20 years at Accenture across the UK and the UAE.
    • One team for ADGM, the DIFC, the federal UAE law and Saudi Arabia.

    Proof

    Client names are shared on request, subject to client approval.

    § 07Questions

    Frequently asked questions

    Do we need a DPO in ADGM?

    Under the ADGM Data Protection Regulations 2021, a DPO is mandatory for public authorities, for organisations whose core activities need regular and systematic monitoring of individuals on a large scale, and for organisations whose core activities involve large scale processing of special category data. Others may appoint one voluntarily.

    Can an external provider act as our DPO in ADGM?

    Yes. The regulations allow the DPO to be a staff member or to fulfil the tasks under a service contract. WLC can be appointed in this way, with Simon Leadbetter as the lead.

    Can one DPO cover our whole group?

    Yes, provided the DPO is easily accessible from each entity. Many groups combine an ADGM entity with entities in Europe or elsewhere in the Gulf, and WLC can act for all of them.

    How close are the ADGM regulations to the GDPR?

    Very close. The ADGM Data Protection Regulations 2021 were modelled on the GDPR, including the DPO triggers, data subject rights, DPIAs and breach notification. A GDPR programme is a strong starting point, but ADGM specific points such as transfers and filings still need attention.

    Who regulates data protection in ADGM?

    The ADGM Office of Data Protection, led by the Commissioner of Data Protection. It supervises compliance, handles complaints and can issue fines.

    What does the DPO do in ADGM?

    The DPO informs and advises the organisation, monitors compliance, advises on DPIAs, cooperates with the Office of Data Protection and acts as the contact point for individuals. WLC also maintains records of processing and supports breach response.

    Does the UAE federal PDPL apply in ADGM?

    No. ADGM has its own data protection regulations and regulator, so the federal law does not apply there. Groups with mainland UAE entities may need to comply with both.

    Does appointing an external DPO transfer our legal responsibility?

    No. The controller remains responsible for compliance. The DPO advises and monitors, while decisions about processing stay with your organisation.

    § 09Get in touch

    Talk to our ADGM DPO team

    Last reviewed: by Simon Leadbetter, Associate Partner, GCC