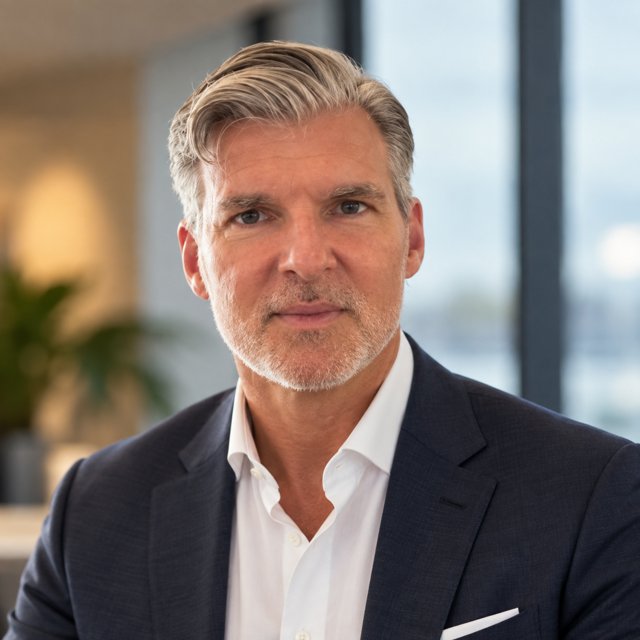
Simon Leadbetter
Associate Partner, GCC
GCC practice · Saudi Arabia
Saudi Arabia now runs one of the most demanding compliance environments in the region. Data protection is enforced, cybersecurity controls are audited, and financial regulators expect a working compliance function with evidence behind it.
We help organisations in the Kingdom, and the international groups that operate there, build one framework that answers to every regulator at once.
Trusted data and responsible technology are part of the national plan. Good governance is how organisations take part in it.
The reference point for responsible AI in the Kingdom. We turn the principles into roles, controls and review steps for each AI system.
National data management and governance standards that shape how public bodies and their suppliers classify, share and protect data.
Saudi Data and AI Authority
Supervises the Personal Data Protection Law and its implementing regulations, and sets AI ethics guidance.
National Cybersecurity Authority
Issues the Essential Cybersecurity Controls and sector controls for government bodies, critical infrastructure and their suppliers.
Saudi Central Bank
Sets the Cyber Security Framework, the Business Continuity Management Framework and compliance rules for financial institutions.
Capital Market Authority
Issues the Corporate Governance Regulations for listed companies and rules for capital market institutions.
National Data Management Office
Sets national data management and governance standards, under SDAIA.
The grace period has ended. SDAIA expects registration, records of processing, breach reporting and DPO appointments where required.
SDAIA has consulted on amendments to the PDPL implementing regulations. We track the consultation and will explain what changes once the final text is published.
Associate Partner, GCC
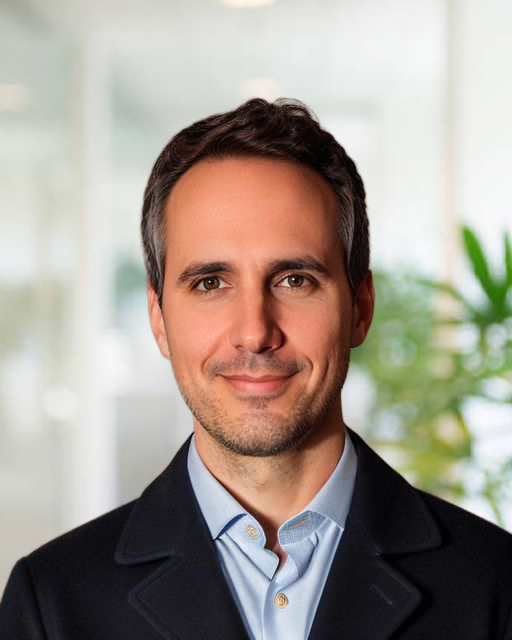
Associate Partner, Head of AI and Transformation
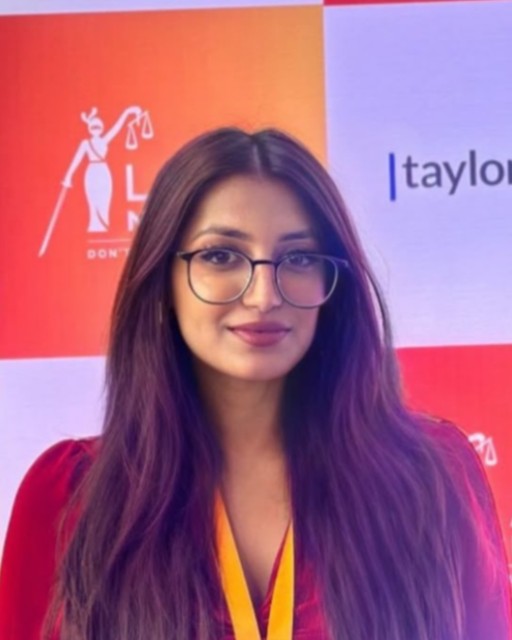
Junior Associate, Governance, Compliance, and Data Protection
Meet the full team.
Associate Partner, GCC
WhatsApp or call +971 558 701 959, or send us a message.